


The Future of Network Security: Identity, Segmentation & Securing the Edge
BRATISLAVA, MONTREAL – ESET Research has discovered that more than ten different advanced persistent threat (APT) groups are exploiting the recent Microsoft Exchange vulnerabilities to compromise email servers. ESET has identified more than 5,000 email servers that have been affected by malicious activity related to the incident. The servers belong to organizations – businesses and governments alike – from around the world, including high-profile ones. Thus, the threat is not limited to the widely reported Hafnium group.
In early March, Microsoft released patches for Exchange Server 2013, 2016 and 2019 that fix a series of pre-authentication remote code execution (RCE) vulnerabilities. The vulnerabilities allow an attacker to take over any reachable Exchange server, without the need to know any valid account credentials, making internet-connected Exchange servers especially vulnerable.
“The day after the release of the patches, we started to observe many more threat actors scanning and compromising Exchange servers en masse. Interestingly, all of them are APT groups focused on espionage, except one outlier that seems related to a known coin-mining campaign. However, it is inevitable that more and more threat actors, including ransomware operators, will have access to the exploits sooner or later,” says Matthieu Faou, who is leading ESET’s research effort into the recent Exchange vulnerability chain. ESET researchers noticed that some APT groups were exploiting the vulnerabilities even before the patches were released. “This means we can discard the possibility that those groups built an exploit by reverse engineering Microsoft updates,” adds Faou.
ESET telemetry flagged the presence of webshells (malicious programs or scripts that allow remote control of a server via a web browser) on more than 5,000 unique servers in over 115 countries.
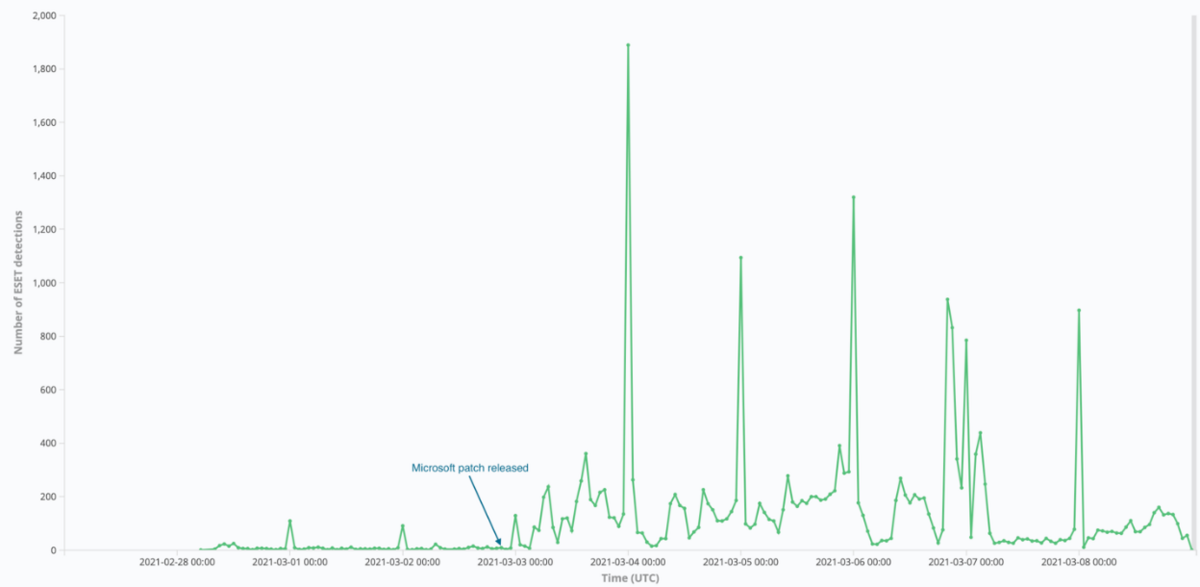
ESET hourly detections for webshells dropped via CVE-2021-26855 – one of the recent Exchange vulnerabilities
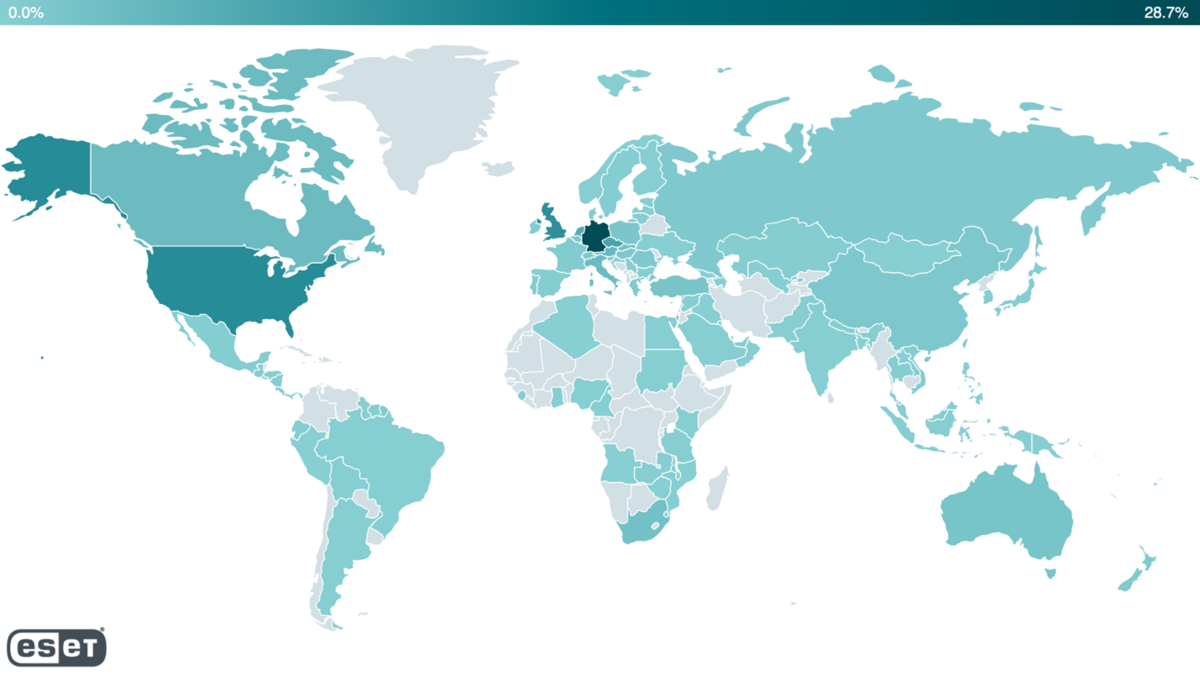
Proportion of webshell detections by country (2021-02-28 to 2021-03-09)
ESET has identified more than ten different threat actors that likely leveraged the recent Microsoft Exchange RCE vulnerabilities in order to install malware like webshells and backdoors on victims’ email servers. In some cases, several threat actors were targeting the same organization.
The identified threat groups and behavior clusters are:
- Tick – compromised the web server of a company based in East Asia that provides IT services. As in the case of LuckyMouse and Calypso, the group likely had access to an exploit prior to the release of the patches.
- LuckyMouse – compromised the email server of a governmental entity in the Middle East. This APT group likely had an exploit at least one day before the patches were released, when it was still a zero day.
- Calypso – compromised the email servers of governmental entities in the Middle East and in South America. The group likely had access to the exploit as a zero day. In the following days, Calypso operators targeted additional servers of governmental entities and private companies in Africa, Asia and Europe.
- Websiic – targeted seven email servers belonging to private companies (in the domains of IT, telecommunications and engineering) in Asia and a governmental body in Eastern Europe. ESET named this new cluster of activity as Websiic.
- Winnti Group – compromised the email servers of an oil company and a construction equipment company in Asia. The group likely had access to an exploit prior to the release of the patches.
- Tonto Team – compromised the email servers of a procurement company and of a consulting company specialized in software development and cybersecurity, both based in Eastern Europe.
- ShadowPad activity – compromised the email servers of a software development company based in Asia and a real estate company based in the Middle East. ESET detected a variant of the ShadowPad backdoor dropped by an unknown group.
- The “Opera” Cobalt Strike – targeted around 650 servers, mostly in the US, Germany, the UK and other European countries just a few hours after the patches were released.
- IIS backdoors – ESET observed IIS backdoors installed via webshells used in these compromises on four email servers located in Asia and South America. One of the backdoors is publicly known as Owlproxy.
- Mikroceen – compromised the exchange server of a utility company in Central Asia, which is the region this group typically targets.
- DLTMiner – ESET detected the deployment of PowerShell downloaders on multiple email servers that were previously targeted using the Exchange vulnerabilities. The network infrastructure used in this attack is linked to a previously reported coin-mining campaign.
“It is now clearly beyond prime time to patch all Exchange servers as soon as possible. Even those not directly exposed to the internet should be patched. In case of compromise, admins should remove the webshells, change credentials and investigate for any additional malicious activity. The incident is a very good reminder that complex applications such as Microsoft Exchange or SharePoint should not be open to the internet,” advises Faou.
For more technical details about these attacks exploiting the recent Exchange vulnerabilities, read the blogpost “Exchange servers under siege from at least 10 APT groups” on WeLiveSecurity. Make sure to follow ESET Research on Twitter for the latest news from ESET Research.