跳過至內容

Reducing Attack through the Zero Trust Solution

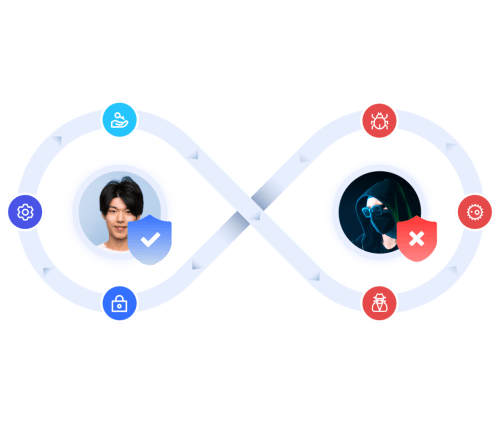
Adhering to the principles of zero trust, SealSuite designs secure access rules based on employee roles. Through continuous trust assessment, dynamic access control, multi-factor authentication, traffic decryption and encryption, and audit logs, we effectively mitigate security risks posed by untrusted individuals/devices accessing the network indiscriminately.

Never Trust, Always Verify

With the rise of remote work and cloud applications, enterprise network environments have become increasingly complex. In response, the zero trust principle of continuous verification and dynamic authorization has emerged as a new security paradigm.

320-solution-zero-trust-feature-icon-1.eb96c0b6

Secure Network
Access

Covering Virtual Private Networks (VPN), Wi-Fi, and wired networks, we implement dynamic access control to reduce exposure to security risks in all aspects of networks.

320-solution-zero-trust-feature-icon-2.9a84d56a

Protecting Various
Business Systems

Whether deployed in public clouds, private clouds, or on-premises data centers, our solution enables seamless and secure access from anywhere.

320-solution-zero-trust-feature-icon-3.b210c861

Balancing Security
and User Experience

With one-click access to internal networks and applications, SealSuite enhances employee office experience while defaulting to secure verification.
Comprehensive Identity-Centric Approach

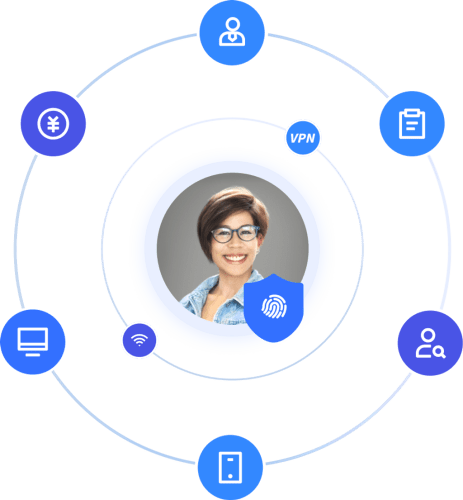
Zero trust represents a continuously evolving network security paradigm, transforming the traditional network-based trust model into an identity-based trust model. Through identity governance, SealSuite connects comprehensive identity-centricity of entities such as devices, users, and applications and establishes a new security boundary for office networks.

Secure Business Access

Both networks and applications are critical business resources that enterprises need to protect, especially in today’s environment where access requests can originate from any time and place. To mitigate risks and prevent attacks or misuse of business resources, enterprises must implement measures such as least privilege access permissions, encrypted traffic, enforcing identity authentication, and conducting device security checks. These practices help to reduce exposure and safeguard business resources effectively.

Continuous Risk Assessment

Based on identity as the foundation of trust, SealSuite ensures that all access entities (users, devices, environments, etc.) undergo comprehensive and continuous trust verification. This includes multi-factor authentication, baseline checks, endpoint threat detection, data leak detection, and more, enabling real-time insight into internal network security risks.

Dynamic Access Control

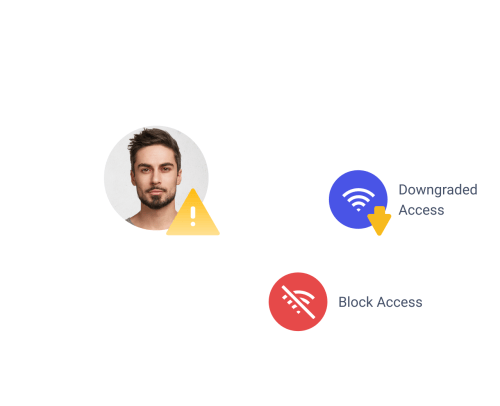
By leveraging proprietary engines that respond to enterprise security management policies, SealSuite automates the downgrading or prohibition of network connections and application access permissions for risky devices, thereby preventing the spread of threats. Event alerts and log analysis capabilities aid in auditing the effectiveness of policies, ensuring compliance with regulatory requirements.

聯絡我們

探索更多

安排示範、開始免費試用、要求報價等

We are here to assist you every step of the way.