

Research: Exploiting Insecure Debugger Console (OC)
Introduction
In addition to hosting millions of lines of code, Github contains a ton of secrets hidden in the depths of various repositories. These secrets are the product of developers unknowingly pushing their credentials, server secrets, passwords, etc. to the repository in addition to their code.
These secrets can be found with special Github search queries also called Github Dorks. A good collection of Github dorks is available here: https://github.com/techgaun/github-dorks
Let’s go through a couple examples of these to find secrets.
Dork 1 – filename:sftp-config.json
The file sftp-config.json is created by sublime text editor. Many developers prefer sublime text for remote development. For this purpose, sftp package in sublime comes handy. Sftp can be used with both password and/or key based authentication.
Once you setup the SFTP in sublime, sftp-config.json file is created as following:
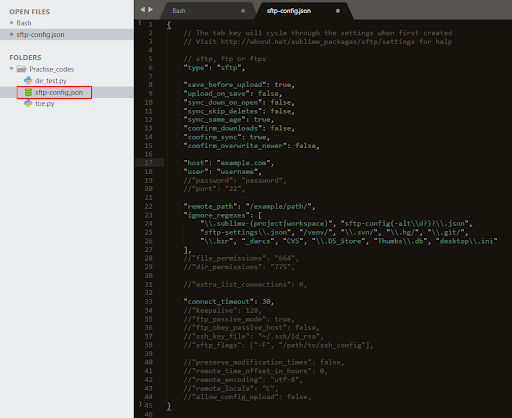
This file contains sensitive information such as username, password, and IP address to connect.
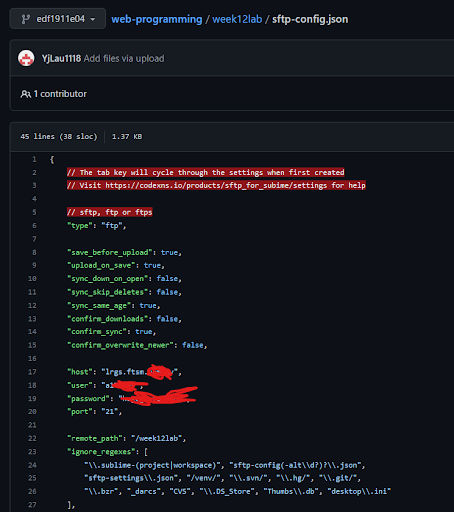
So, if we search in github for sftp-config.json, we get several results, one of which is a web-programming project that contains credentials in plain text.
Dork 2 – filename:config.php dbpasswd
It is very common for php applications to hardcode database credentials. Usually the config.php file is used to provide configuration details for a php application which will be used to establish a database connection. So when we use this github dork, we get many results with php projects containing hardcoded credentials.
One example is valueclickbrands project.

Attackers can take advantage of this information disclosure bug to hijack the database completely and deal more damage.
Key Takeaway
Before making any project public, make sure the Github repository as well as previous commit branches does not contain hardcoded credentials and config files.
#github #dorks