


Keepit Responsible AI Integration
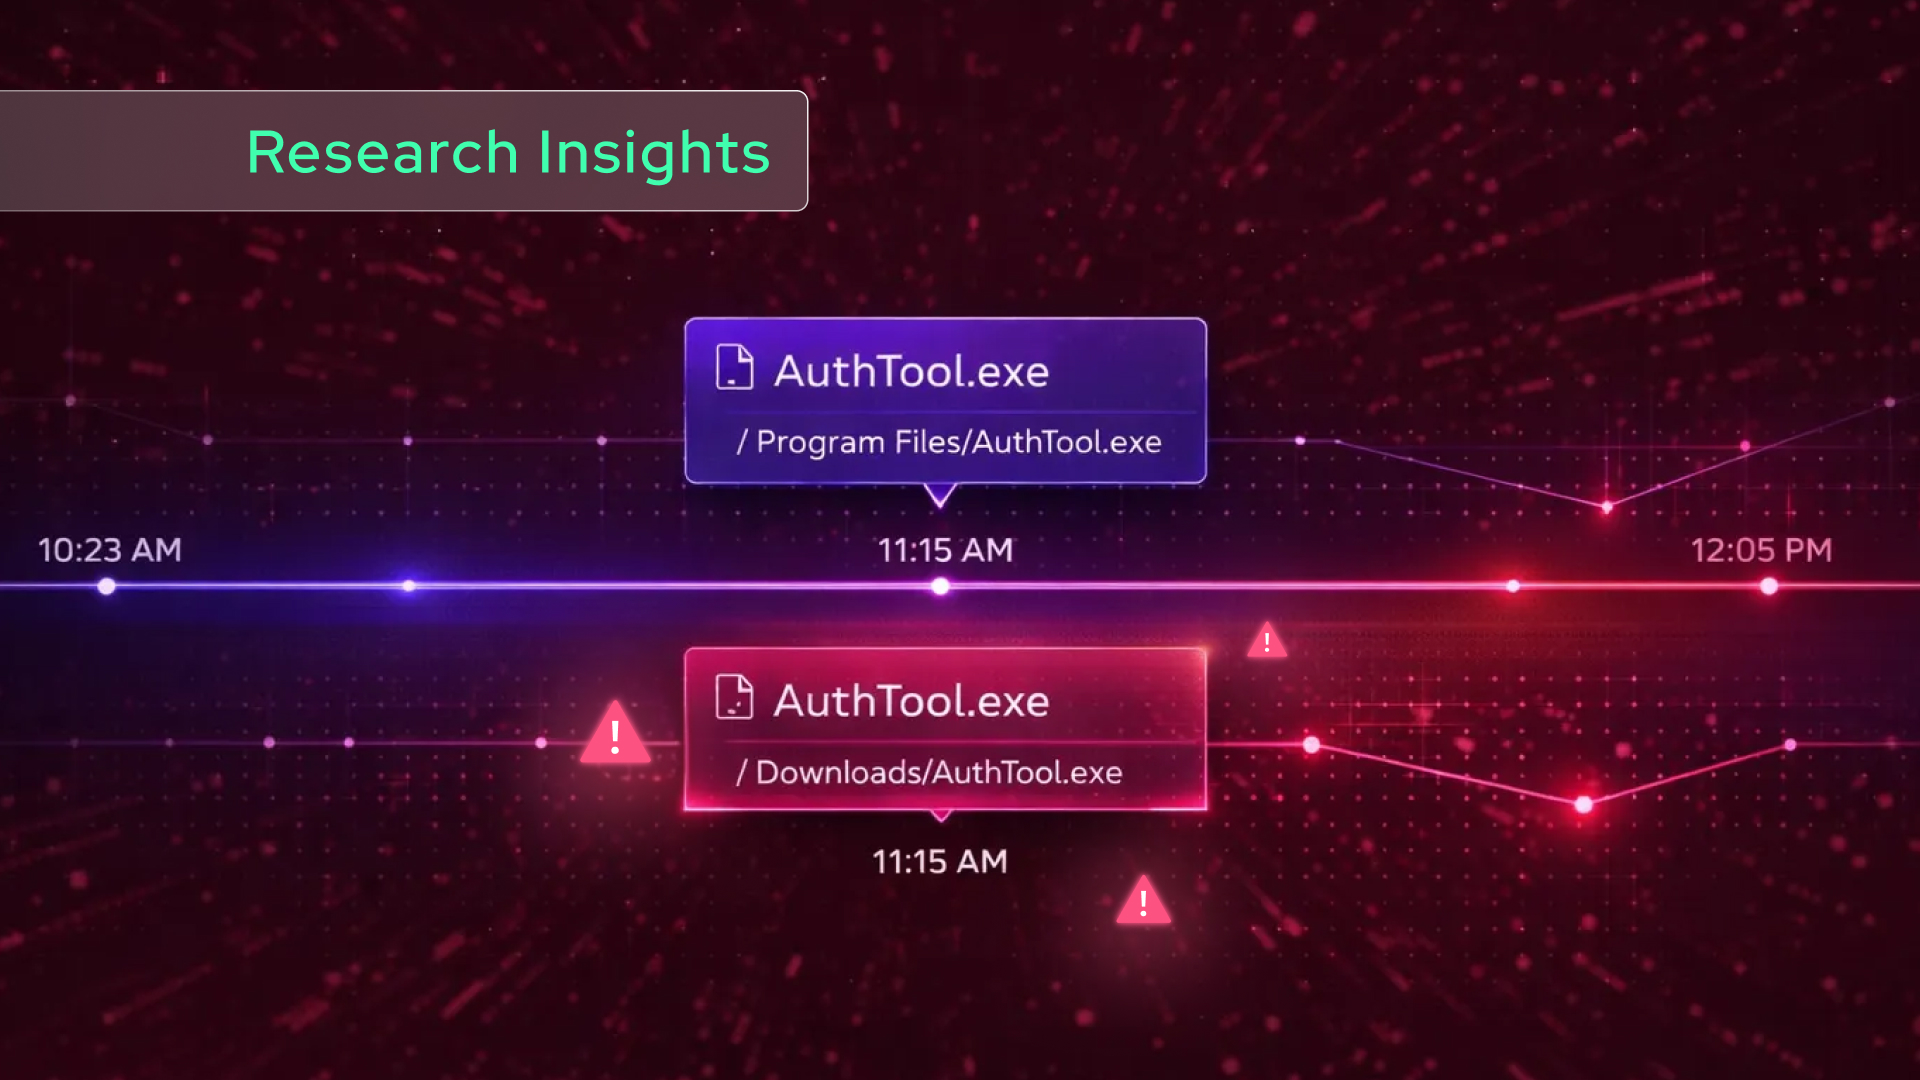
The “Black Box” Problem: AI Skills are becoming a primary infection vector. Attackers leverage manufactured trust and “name-squatting” to bypass security logic by targeting user common sense.
The Collision: Legitimate vs. Malicious
Legitimate AuthTool
- Source: N-able Cove Backup
- Status: Documented & Signed
- Path:
C:\Program Files\...
Malicious AuthTool
- Source: Fake “Reddit-Trends” Skill
- Status: Unsigned Trojan
- Path:
C:\Users\[User]\Downloads
The Anatomy of the Attack
The attack follows a classic Trojan horse pattern: wrapping a malicious payload in a high-demand productivity tool (Reddit automation).
- AV Evasion: The payload is delivered via a password-protected ZIP (Password:
1234) to blindside automated scanners. - Mac Execution: Uses
base64 -d | shto execute shellcode directly into the kernel. - Social Engineering: Instructions tell the user to “Run AuthTool.exe BEFORE starting the skill,” establishing the binary as a trusted prerequisite.
結論
Thorough forensic profiling of legitimate software remains the best defense. Analysts must verify not just the filename, but the hash, path, and signing authority of every execution event.