


Portnox and SentinelOne Partner for Real-Time Access Control
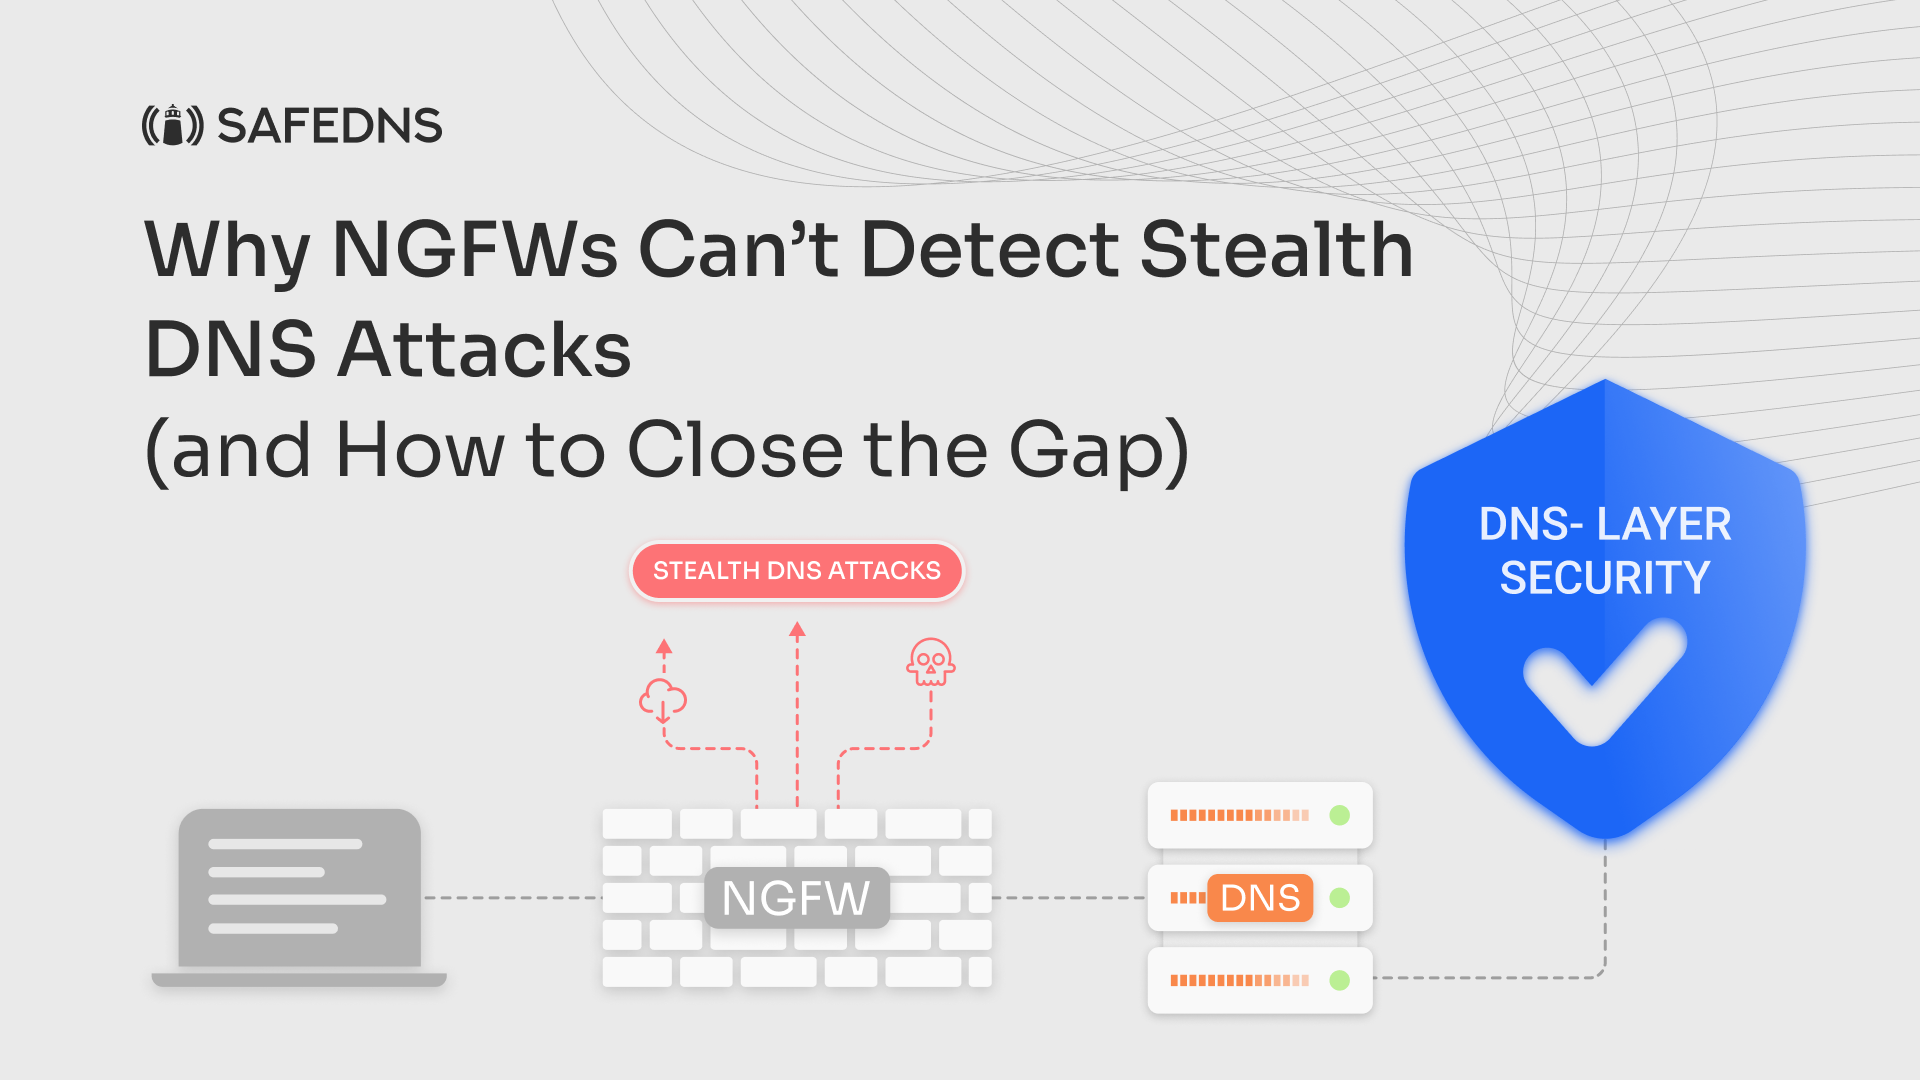
This article discusses a significant security gap in modern network defenses: the inability of Next-Generation Firewalls (NGFWs) to detect highly evasive DNS-based attacks. While NGFWs are effective against many threats, they are often blind to malicious activity hidden within DNS traffic, leaving a critical vulnerability that cybercriminals are actively exploiting.
The Evasion Tactic: How Attackers Use DNS
Attackers use a technique called DNS tunneling to create a covert communication channel. They encode malicious traffic—such as command-and-control (C2) signals or data exfiltration—within standard DNS queries and responses. Because DNS is an essential part of network communication and is often considered a “trusted” protocol, NGFWs and other security tools frequently allow this traffic to pass through uninspected. This provides a perfect, low-detection pathway for a stealth attack.
Why NGFWs Fall Short
Next-Generation Firewalls excel at inspecting the content of data packets, but they often struggle with DNS traffic for several reasons: they typically only inspect DNS requests, not the full response; they cannot analyze the deep-level content of a query to detect malicious payloads; and they are not designed to identify the behavioral patterns of DNS tunneling, which involves an unusually high volume of DNS requests to a single domain.
Closing the Security Gap
To combat this threat, the article recommends a multi-layered security approach. This includes implementing a dedicated DNS security solution that is designed specifically to analyze DNS queries and responses in real-time. These specialized tools can perform deep packet inspection, apply behavioral analysis to detect DNS tunneling, and block malicious traffic before it reaches the network. By adding a dedicated DNS security layer, organizations can effectively close the gap that NGFWs leave open and create a more resilient defense against advanced cyberattacks.